- Blog Categories
- Project Management
- Agile Management
- IT Service Management
- Cloud Computing
- Business Management
- BI And Visualisation
- Quality Management
- Cyber Security
- DevOps
- Most Popular Blogs
- PMP Exam Schedule for 2025: Check PMP Exam Date
- Top 60+ PMP Exam Questions and Answers for 2025
- PMP Cheat Sheet and PMP Formulas To Use in 2025
- What is PMP Process? A Complete List of 49 Processes of PMP
- Top 15+ Project Management Case Studies with Examples 2025
- Top Picks by Authors
- Top 170 Project Management Research Topics
- What is Effective Communication: Definition
- How to Create a Project Plan in Excel in 2025?
- PMP Certification Exam Eligibility in 2025 [A Complete Checklist]
- PMP Certification Fees - All Aspects of PMP Certification Fee
- Most Popular Blogs
- CSM vs PSM: Which Certification to Choose in 2025?
- How Much Does Scrum Master Certification Cost in 2025?
- CSPO vs PSPO Certification: What to Choose in 2025?
- 8 Best Scrum Master Certifications to Pursue in 2025
- Safe Agilist Exam: A Complete Study Guide 2025
- Top Picks by Authors
- SAFe vs Agile: Difference Between Scaled Agile and Agile
- Top 21 Scrum Best Practices for Efficient Agile Workflow
- 30 User Story Examples and Templates to Use in 2025
- State of Agile: Things You Need to Know
- Top 24 Career Benefits of a Certifed Scrum Master
- Most Popular Blogs
- ITIL Certification Cost in 2025 [Exam Fee & Other Expenses]
- Top 17 Required Skills for System Administrator in 2025
- How Effective Is Itil Certification for a Job Switch?
- IT Service Management (ITSM) Role and Responsibilities
- Top 25 Service Based Companies in India in 2025
- Top Picks by Authors
- What is Escalation Matrix & How Does It Work? [Types, Process]
- ITIL Service Operation: Phases, Functions, Best Practices
- 10 Best Facility Management Software in 2025
- What is Service Request Management in ITIL? Example, Steps, Tips
- An Introduction To ITIL® Exam
- Most Popular Blogs
- A Complete AWS Cheat Sheet: Important Topics Covered
- Top AWS Solution Architect Projects in 2025
- 15 Best Azure Certifications 2025: Which one to Choose?
- Top 22 Cloud Computing Project Ideas in 2025 [Source Code]
- How to Become an Azure Data Engineer? 2025 Roadmap
- Top Picks by Authors
- Top 40 IoT Project Ideas and Topics in 2025 [Source Code]
- The Future of AWS: Top Trends & Predictions in 2025
- AWS Solutions Architect vs AWS Developer [Key Differences]
- Top 20 Azure Data Engineering Projects in 2025 [Source Code]
- 25 Best Cloud Computing Tools in 2025
- Most Popular Blogs
- Company Analysis Report: Examples, Templates, Components
- 400 Trending Business Management Research Topics
- Business Analysis Body of Knowledge (BABOK): Guide
- ECBA Certification: Is it Worth it?
- Top Picks by Authors
- Top 20 Business Analytics Project in 2025 [With Source Code]
- ECBA Certification Cost Across Countries
- Top 9 Free Business Requirements Document (BRD) Templates
- Business Analyst Job Description in 2025 [Key Responsibility]
- Business Analysis Framework: Elements, Process, Techniques
- Most Popular Blogs
- Best Career options after BA [2025]
- Top Career Options after BCom to Know in 2025
- Top 10 Power Bi Books of 2025 [Beginners to Experienced]
- Power BI Skills in Demand: How to Stand Out in the Job Market
- Top 15 Power BI Project Ideas
- Top Picks by Authors
- 10 Limitations of Power BI: You Must Know in 2025
- Top 45 Career Options After BBA in 2025 [With Salary]
- Top Power BI Dashboard Templates of 2025
- What is Power BI Used For - Practical Applications Of Power BI
- SSRS Vs Power BI - What are the Key Differences?
- Most Popular Blogs
- Data Collection Plan For Six Sigma: How to Create One?
- Quality Engineer Resume for 2025 [Examples + Tips]
- 20 Best Quality Management Certifications That Pay Well in 2025
- Six Sigma in Operations Management [A Brief Introduction]
- Top Picks by Authors
- Six Sigma Green Belt vs PMP: What's the Difference
- Quality Management: Definition, Importance, Components
- Adding Green Belt Certifications to Your Resume
- Six Sigma Green Belt in Healthcare: Concepts, Benefits and Examples
- Most Popular Blogs
- Latest CISSP Exam Dumps of 2025 [Free CISSP Dumps]
- CISSP vs Security+ Certifications: Which is Best in 2025?
- Best CISSP Study Guides for 2025 + CISSP Study Plan
- How to Become an Ethical Hacker in 2025?
- Top Picks by Authors
- CISSP vs Master's Degree: Which One to Choose in 2025?
- CISSP Endorsement Process: Requirements & Example
- OSCP vs CISSP | Top Cybersecurity Certifications
- How to Pass the CISSP Exam on Your 1st Attempt in 2025?
- Most Popular Blogs
- Top 7 Kubernetes Certifications in 2025
- Kubernetes Pods: Types, Examples, Best Practices
- DevOps Methodologies: Practices & Principles
- Docker Image Commands
- Top Picks by Authors
- Best DevOps Certifications in 2025
- 20 Best Automation Tools for DevOps
- Top 20 DevOps Projects of 2025
- OS for Docker: Features, Factors and Tips
- More
- Agile & PMP Practice Tests
- Agile Testing
- Agile Scrum Practice Exam
- CAPM Practice Test
- PRINCE2 Foundation Exam
- PMP Practice Exam
- Cloud Related Practice Test
- Azure Infrastructure Solutions
- AWS Solutions Architect
- IT Related Pratice Test
- ITIL Practice Test
- Devops Practice Test
- TOGAF® Practice Test
- Other Practice Test
- Oracle Primavera P6 V8
- MS Project Practice Test
- Project Management & Agile
- Project Management Interview Questions
- Release Train Engineer Interview Questions
- Agile Coach Interview Questions
- Scrum Interview Questions
- IT Project Manager Interview Questions
- Cloud & Data
- Azure Databricks Interview Questions
- AWS architect Interview Questions
- Cloud Computing Interview Questions
- AWS Interview Questions
- Kubernetes Interview Questions
- Web Development
- CSS3 Free Course with Certificates
- Basics of Spring Core and MVC
- Javascript Free Course with Certificate
- React Free Course with Certificate
- Node JS Free Certification Course
- Data Science
- Python Machine Learning Course
- Python for Data Science Free Course
- NLP Free Course with Certificate
- Data Analysis Using SQL
CompTIA Security+ SY0-701 Exam Domains: Complete Breakdown of All 5 Domains
Updated on Oct 11, 2026 | 1.04K+ views
Share:
Table of Contents
View all
Quick Overview
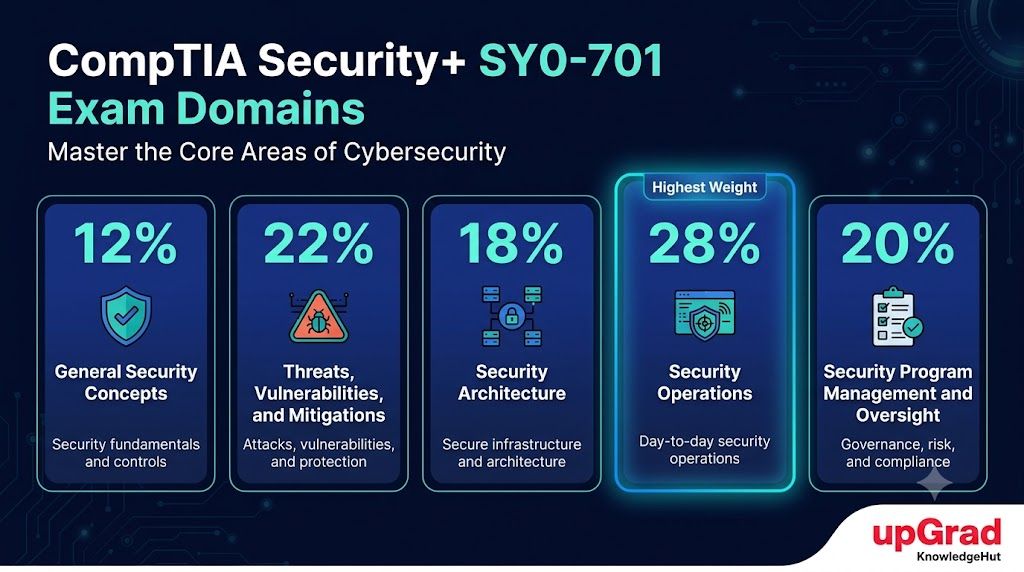
- The CompTIA Security+ SY0-701 exam domains include five areas: General Security Concepts (12%), Threats, Vulnerabilities, and Mitigations (22%), Security Architecture (18%), Security Operations (28%), and Security Program Management and Oversight (20%).
- General Security Concepts covers core security principles, including security controls, the CIA triad, authentication, authorization, cryptography, PKI, and Zero Trust.
- Threats, Vulnerabilities, and Mitigations focuses on common cyber threats, attack vectors, vulnerabilities, indicators of compromise, and ways to reduce security risks.
- Security Architecture, Security Operations, and Program Management cover practical security responsibilities, from secure infrastructure and monitoring to incident response, governance, risk, and compliance.
- This guide covers all five CompTIA Security+ SY0-701 exam domains, their weightage, key topics, and what you need to know to prepare for the exam.
Ready to prepare for the Security+ exam with structured training? Explore the CompTIA Security+ Certification Training Course to build your cybersecurity knowledge and prepare with focused guidance.
Master the Right Skills & Boost Your Career
Avail your free 1:1 mentorship session
What are the CompTIA Security+ SY0-701 exam domains?
The SY0-701 exam consists of five domains:
SY0-701 domain |
Domain name |
Exam weight |
Main focus |
| 1.0 | General Security Concepts | 12% | Security fundamentals and controls |
| 2.0 | Threats, Vulnerabilities, and Mitigations | 22% | Threats, attacks, vulnerabilities, and mitigations |
| 3.0 | Security Architecture | 18% | Secure infrastructure and architecture |
| 4.0 | Security Operations | 28% | Day-to-day security operations |
| 5.0 | Security Program Management and Oversight | 20% | Governance, risk, compliance, and oversight |
Also Read: How to Study for CompTIA Security+: An 8-Week Study Plan
Domain 1: General Security Concepts (12%)
General Security Concepts covers the basic principles that are required to understand all other topics covered in security. The domain includes the basic concepts, terminologies, and security principles in various areas of cybersecurity.
Some important topics are as follows:
- Security controls: You need to be well-versed with preventative controls, detective controls, corrective controls, deterrent controls, compensatory controls, and directive controls.
- The CIA triad: Get a good understanding of what confidentiality, integrity, and availability have to offer in terms of information and systems security.
- Authentication and authorization: Learn about the differences between authentication and authorization.
- Zero Trust: Acquire an insight into some basic principles of zero trust that involve continuous user, device, and request verification.
- Cryptography: Learn about encryption fundamentals, hashing, digital signatures, and certificates.
- Public Key Infrastructure (PKI): Learn about the functions of certificates and certificate authorities.
- Physical security: Learn about the controls used to protect physical assets such as buildings and equipment.
Also Read: Security+ Exam Preparation Plan for Working Professionals
Domain 2: Threats, Vulnerabilities, and Mitigations (22%)
Cybersecurity experts spend considerable amounts of time identifying and mitigating threats. That's why this domain receives a lot of attention in the exam. Domain 2 encompasses the threats which the organization could face, the vulnerabilities which could be exploited by the threats, and the techniques for risk mitigation.
Key areas include:
- Threat actors: Learn about different types of attackers and their motivations.
- Threat vectors and attack surfaces: Understand how attackers might get access to your systems or networks.
- Social engineering: Learn more about different forms of manipulation like phishing, spear-phishing, whaling, vishing, smishing, and others.
- Malware: Understand common forms of malicious software and their potential impact.
- Application and network attacks: Learn the basic concepts behind attacks such as injection, denial of service, and password attacks.
- Vulnerabilities: Understand common weaknesses in applications, systems, configurations, and networks.
- Indicators of compromise: Learn how security teams can identify signs that an attack may have occurred.
- Mitigation techniques: Understand how security controls and defensive measures can reduce threats and vulnerabilities.
Want to build practical skills in AI beyond cybersecurity? Explore the Applied Agentic AI Certification Course to learn how to design and apply AI agents in real-world workflows.
Domain 3: Security Architecture (18%)
This domain concentrates on secure systems, networks, and infrastructure design and maintenance. As opposed to considering each security control in isolation, here you will have to look beyond them and see their interactions.
The main topics to study are:
- Enterprise architecture: Understand how security can be incorporated into organizational infrastructure.
- Cloud environments: Review the basics of cloud security and shared responsibility.
- Network segmentation: Understand how separating networks or systems can limit unauthorized access and reduce the impact of an attack.
- Infrastructure security: Learn how servers, networks, applications, and other infrastructure components can be protected.
- Data protection: Consider various ways to secure data throughout all its life cycle stages, e.g. when it's stored and transferred.
- Resilience: Study the concepts that help organizations keep functioning in case their systems fail.
- IoT and specialized systems: Consider the security challenges related to connected and specialized devices.
Also Read: What Is PCI DSS Compliance and Why Do Organizations Need It?
Domain 4: Security Operations (28%)
This area is considered the most important area as the weight of Security Operations in the SY0-701 examination is the highest one.
In this area, the candidate should study about activities that security specialists undertake regularly to protect systems and respond to security threats.
Key topics include:
- Security monitoring: Learn about methods organizations use for monitoring suspicious activity.
- Asset management: Learn how to recognize and manage security devices, software, and other assets.
- Vulnerability management: Review how vulnerabilities are identified, assessed, prioritized, and addressed.
- Identity and access management: Understand access controls, authentication methods, and account management.
- Endpoint security: Learn how endpoints such as workstations, mobile devices can be secured.
- Logging and monitoring: Learn reasons for collection of logs and how these logs can help to conduct security investigations.
- Incident response: Learn steps of incident detection, handling and recovery.
- Digital forensics: Learn how to collect and analyze evidence obtained after a security threat occurs.
- Automation and orchestration: Learn how security teams can automate repetitive tasks and coordinate security workflows.
Also Read: Operational Technology (OT) Security
Domain 5: Security Program Management and Oversight (20%)
Domain 5 looks at how organizations manage, govern, and oversee their security programs. It moves beyond purely technical controls and focuses on how security decisions support business requirements and reduce organizational risk.
The main areas to study include:
- Security governance: Understand policies, standards, procedures, guidelines, and security roles.
- Risk management: Learn how organizations identify, assess, prioritize, and respond to security risks.
- Third-party risk: Understand the security risks associated with vendors, contractors, suppliers, and other external partners.
- Compliance and privacy: Review regulatory requirements, legal considerations, audits, and privacy responsibilities.
- Security policies: Understand how organizations document security expectations and requirements.
- Security awareness: Learn how employee training can reduce human-related security risks.
- Business continuity and disaster recovery: Understand how organizations prepare to maintain or restore critical operations after a disruption.
Looking to expand your AI skills alongside cybersecurity knowledge? Explore the Generative AI and Prompt Engineering Course for Professionals to build practical skills in generative AI and effective prompting.
Conclusion
The CompTIA Security+ SY0-701 exam covers five domains that test your understanding of security concepts, cyber threats, secure architecture, security operations, and risk management. Knowing what each domain includes helps you prepare with a clearer plan and focus on the topics you need to strengthen.
Review the official exam objectives, practise questions regularly, and revisit areas where you make mistakes. With consistent preparation and a solid understanding of all five domains, you can approach the Security+ exam with greater confidence.
Have A Query? Get in Touch With Our Customer Support | upGrad KnowledgeHut
Frequently Asked Questions (FAQs)
1. What are the CompTIA Security+ SY0-701 exam domains?
The SY0-701 exam has five domains: General Security Concepts (12%), Threats, Vulnerabilities, and Mitigations (22%), Security Architecture (18%), Security Operations (28%), and Security Program Management and Oversight (20%). Together, these domains cover the technical, operational, and governance aspects of cybersecurity tested in Security+.
2. Which domain is the hardest in Security+ SY0-701?
There is no single hardest domain for every candidate, but Security Operations (Domain 4) can be challenging because it covers a wide range of practical topics, including monitoring, vulnerability management, incident response, identity and access management, and digital forensics. Your experience with hands-on security tasks can affect which domain feels most difficult.
3. What should I study first for Security+ SY0-701?
Start with General Security Concepts to build a foundation in areas such as security controls, the CIA triad, authentication, authorization, cryptography, and Zero Trust. Then move to Threats, Vulnerabilities, and Mitigations and Security Operations, which cover major technical areas of the exam.
4. Which domains contain the most PBQs?
CompTIA does not publish an official breakdown showing how many performance-based questions (PBQs) come from each domain. However, PBQs can test practical skills covered across multiple domains, particularly areas such as Security Operations, Security Architecture, and Threats, Vulnerabilities, and Mitigations. Prepare for scenario-based tasks across all five domains.
5. What changed from SY0-601 to SY0-701?
SY0-701 reorganized the exam into five domains and places greater emphasis on areas such as cloud security, automation, security operations, governance, and newer security practices. The domain structure and objectives also changed from SY0-601, so candidates should use the current SY0-701 objectives rather than an older SY0-601 study guide.
6. What threats appear on Security+ SY0-701?
SY0-701 covers threats such as malware, phishing and other social engineering attacks, password attacks, network attacks, application attacks, and attacks involving vulnerable systems or configurations. You should also understand different threat actors, attack vectors, indicators of compromise, and appropriate mitigation techniques.
7. Does SY0-701 include cloud security?
Yes. Cloud security is included in SY0-701, particularly within Security Architecture and related security operations topics. Candidates should understand cloud deployment and service models, shared responsibility, secure cloud architecture, and security considerations when organizations use cloud-based infrastructure and services.
8. How should beginners approach the five domains?
Beginners should first learn General Security Concepts because it introduces security terminology and principles used throughout the exam. Next, study the remaining domains one at a time, practice questions after each topic, and review incorrect answers. Give additional study time to areas where practice results show knowledge gaps.
9. How many questions come from each Security+ domain?
CompTIA provides domain percentages rather than a fixed number of questions for each domain. The five domains represent 12%, 22%, 18%, 28%, and 20% of the exam respectively, but the actual number of questions from each domain can vary because the exam does not assign a fixed question count to every domain.
10. How much study time should I spend on each domain?
A practical approach is to divide your study time roughly according to the domain weights: 28% for Security Operations, 22% for Threats, Vulnerabilities, and Mitigations, 20% for Security Program Management and Oversight, 18% for Security Architecture, and 12% for General Security Concepts. Adjust these percentages when practice tests show that you need more time in a particular area.
1648 articles published
KnowledgeHut is an outcome-focused global ed-tech company. We help organizations and professionals unlock excellence through skills development. We offer training solutions under the people and proces...
Get Free Consultation
By submitting, I accept the T&C and
Privacy Policy