- Blog Categories
- Project Management
- Agile Management
- IT Service Management
- Cloud Computing
- Business Management
- BI And Visualisation
- Quality Management
- Cyber Security
- DevOps
- Most Popular Blogs
- PMP Exam Schedule for 2026: Check PMP Exam Date
- Top 60+ PMP Exam Questions and Answers for 2026
- PMP Cheat Sheet and PMP Formulas To Use in 2026
- What is PMP Process? A Complete List of 49 Processes of PMP
- Top 15+ Project Management Case Studies with Examples 2026
- Top Picks by Authors
- Top 170 Project Management Research Topics
- What is Effective Communication: Definition
- How to Create a Project Plan in Excel in 2026?
- PMP Certification Exam Eligibility in 2026 [A Complete Checklist]
- PMP Certification Fees - All Aspects of PMP Certification Fee
- Most Popular Blogs
- CSM vs PSM: Which Certification to Choose in 2026?
- How Much Does Scrum Master Certification Cost in 2026?
- CSPO vs PSPO Certification: What to Choose in 2026?
- 8 Best Scrum Master Certifications to Pursue in 2026
- Safe Agilist Exam: A Complete Study Guide 2026
- Top Picks by Authors
- SAFe vs Agile: Difference Between Scaled Agile and Agile
- Top 21 Scrum Best Practices for Efficient Agile Workflow
- 30 User Story Examples and Templates to Use in 2026
- State of Agile: Things You Need to Know
- Top 24 Career Benefits of a Certifed Scrum Master
- Most Popular Blogs
- ITIL Certification Cost in 2026 [Exam Fee & Other Expenses]
- Top 17 Required Skills for System Administrator in 2026
- How Effective Is Itil Certification for a Job Switch?
- IT Service Management (ITSM) Role and Responsibilities
- Top 25 Service Based Companies in India in 2026
- Top Picks by Authors
- What is Escalation Matrix & How Does It Work? [Types, Process]
- ITIL Service Operation: Phases, Functions, Best Practices
- 10 Best Facility Management Software in 2026
- What is Service Request Management in ITIL? Example, Steps, Tips
- An Introduction To ITIL® Exam
- Most Popular Blogs
- A Complete AWS Cheat Sheet: Important Topics Covered
- Top AWS Solution Architect Projects in 2026
- 15 Best Azure Certifications 2026: Which one to Choose?
- Top 22 Cloud Computing Project Ideas in 2026 [Source Code]
- How to Become an Azure Data Engineer? 2026 Roadmap
- Top Picks by Authors
- Top 40 IoT Project Ideas and Topics in 2026 [Source Code]
- The Future of AWS: Top Trends & Predictions in 2026
- AWS Solutions Architect vs AWS Developer [Key Differences]
- Top 20 Azure Data Engineering Projects in 2026 [Source Code]
- 25 Best Cloud Computing Tools in 2026
- Most Popular Blogs
- Company Analysis Report: Examples, Templates, Components
- 400 Trending Business Management Research Topics
- Business Analysis Body of Knowledge (BABOK): Guide
- ECBA Certification: Is it Worth it?
- Top Picks by Authors
- Top 20 Business Analytics Project in 2026 [With Source Code]
- ECBA Certification Cost Across Countries
- Top 9 Free Business Requirements Document (BRD) Templates
- Business Analyst Job Description in 2026 [Key Responsibility]
- Business Analysis Framework: Elements, Process, Techniques
- Most Popular Blogs
- Best Career options after BA [2026]
- Top Career Options after BCom to Know in 2026
- Top 10 Power Bi Books of 2026 [Beginners to Experienced]
- Power BI Skills in Demand: How to Stand Out in the Job Market
- Top 15 Power BI Project Ideas
- Top Picks by Authors
- 10 Limitations of Power BI: You Must Know in 2026
- Top 45 Career Options After BBA in 2026 [With Salary]
- Top Power BI Dashboard Templates of 2026
- What is Power BI Used For - Practical Applications Of Power BI
- SSRS Vs Power BI - What are the Key Differences?
- Most Popular Blogs
- Data Collection Plan For Six Sigma: How to Create One?
- Quality Engineer Resume for 2026 [Examples + Tips]
- 20 Best Quality Management Certifications That Pay Well in 2026
- Six Sigma in Operations Management [A Brief Introduction]
- Top Picks by Authors
- Six Sigma Green Belt vs PMP: What's the Difference
- Quality Management: Definition, Importance, Components
- Adding Green Belt Certifications to Your Resume
- Six Sigma Green Belt in Healthcare: Concepts, Benefits and Examples
- Most Popular Blogs
- Latest CISSP Exam Dumps of 2026 [Free CISSP Dumps]
- CISSP vs Security+ Certifications: Which is Best in 2026?
- Best CISSP Study Guides for 2026 + CISSP Study Plan
- How to Become an Ethical Hacker in 2026?
- Top Picks by Authors
- CISSP vs Master's Degree: Which One to Choose in 2026?
- CISSP Endorsement Process: Requirements & Example
- OSCP vs CISSP | Top Cybersecurity Certifications
- How to Pass the CISSP Exam on Your 1st Attempt in 2026?
- Most Popular Blogs
- Top 7 Kubernetes Certifications in 2026
- Kubernetes Pods: Types, Examples, Best Practices
- DevOps Methodologies: Practices & Principles
- Docker Image Commands
- Top Picks by Authors
- Best DevOps Certifications in 2026
- 20 Best Automation Tools for DevOps
- Top 20 DevOps Projects of 2026
- OS for Docker: Features, Factors and Tips
- More
- Agile & PMP Practice Tests
- Agile Testing
- Agile Scrum Practice Exam
- CAPM Practice Test
- PRINCE2 Foundation Exam
- PMP Practice Exam
- Cloud Related Practice Test
- Azure Infrastructure Solutions
- AWS Solutions Architect
- IT Related Pratice Test
- ITIL Practice Test
- Devops Practice Test
- TOGAF® Practice Test
- Other Practice Test
- Oracle Primavera P6 V8
- MS Project Practice Test
- Project Management & Agile
- Project Management Interview Questions
- Release Train Engineer Interview Questions
- Agile Coach Interview Questions
- Scrum Interview Questions
- IT Project Manager Interview Questions
- Cloud & Data
- Azure Databricks Interview Questions
- AWS architect Interview Questions
- Cloud Computing Interview Questions
- AWS Interview Questions
- Kubernetes Interview Questions
- Web Development
- CSS3 Free Course with Certificates
- Basics of Spring Core and MVC
- Javascript Free Course with Certificate
- React Free Course with Certificate
- Node JS Free Certification Course
- Data Science
- Python Machine Learning Course
- Python for Data Science Free Course
- NLP Free Course with Certificate
- Data Analysis Using SQL
Future of Zero Trust Architecture in 2026: Trends, Benefits, and Challenges
Updated on Oct 12, 2026 | 0.8k+ views
Share:
Table of Contents
View all
Quick Overview
- Future of Zero Trust Architecture in 2026: Zero trust architecture is evolving toward identity based security, continuous verification, and risk based access controls to protect cloud environments, remote workforces, and AI systems.
- Key Trends: AI powered threat detection, passwordless authentication, cloud security, and automated policy enforcement are shaping the future of zero trust.
- Benefits and Challenges: Zero trust improves access control, reduces unauthorized access risks, and strengthens protection against ransomware, but implementation can involve legacy system integration, costs, and user experience challenges.
- This guide explains the future trends, benefits, challenges, and implementation priorities of zero trust architecture in 2026.
As Zero Trust Architecture evolves with AI-driven security and automation, AI Powered Product Management can help professionals understand how AI supports product strategy, risk-informed decision-making, and the development of smarter digital solutions.
Master the Right Skills & Boost Your Career
Avail your free 1:1 mentorship session
What is zero trust architecture?
Zero trust architecture is a cybersecurity approach that requires every access request to be verified before granting access to an application, system, or sensitive data. It does not automatically trust users or devices just because they are connected to a company network.
Instead of relying only on traditional network boundaries, zero trust architecture checks identity, device health, permissions, and the level of risk involved. This helps organizations protect resources across cloud platforms, office networks, and remote working environments.
Core principles of zero trust architecture
Zero trust architecture follows three core principles: verify explicitly, use least privilege access, and assume breach. Together, these principles help organizations make access decisions based on evidence instead of automatically trusting a user or device.
The main principles include:
• Verify explicitly: Confirm the user's identity, device, location, and other relevant security signals before allowing access.
• Use least privilege access: Give users and applications only the permissions they need to complete their tasks, and limit access when it is no longer required.
• Assume breach: Design security controls with the understanding that an attacker may already have entered the environment. Focus on detecting suspicious activity and limiting its impact.
• Monitor continuously: Review access conditions and security signals throughout a session rather than relying entirely on the initial login.
How does zero trust architecture work?
Zero trust architecture evaluates each request to access a protected resource. The decision depends on factors such as who or what is requesting access, the resource being requested, the permissions available, and the current security conditions.
The process generally follows these steps:
• A user, device, application, or service requests access to a resource.
• The organization verifies identity and checks relevant security information.
• Access policies determine whether the request should be allowed, denied, or restricted.
• Security controls enforce the decision and monitor activity.
• If the risk changes, access can be limited or revoked.
This approach helps security teams apply consistent access rules across different systems instead of depending on a single network perimeter.
Policy engine, policy administrator, and policy enforcement point
Three important components help manage access decisions in a zero trust architecture. Each has a separate responsibility, from deciding whether access is appropriate to enforcing that decision.
• Policy engine: Evaluates the access request against security policies and available information. It decides whether to grant, deny, or revoke access.
• Policy administrator: Carries out the policy engine's decision by instructing the relevant controls to establish or terminate access.
• Policy enforcement point: Applies the decision in practice. It permits, monitors, or blocks the connection between the requester and the protected resource.
Continuous verification and least privilege access
Zero trust architecture does not treat authentication as a one time event that guarantees trust for the entire session. Access can be reassessed when user behavior, device status, or other risk signals change.
Continuous verification and least privilege access help organizations keep permissions appropriate.
Key practices include:
• Require suitable authentication before granting access to sensitive applications and data.
• Check device compliance, such as whether required security updates and protections are enabled.
• Limit permissions by role and business requirement.
• Use temporary or time limited privileges for sensitive administrative tasks.
• Reassess access when a session becomes suspicious or its risk level changes.
Assume breach and limit threat movement
The assume breach principle means organizations prepare for the possibility that an attacker has already gained access. Rather than relying on a single defensive boundary, they use multiple controls to contain suspicious activity.
This can involve:
• Separating critical systems into smaller network or application segments.
• Restricting communication between systems that do not need to interact.
• Monitoring unusual login activity and unexpected access to sensitive resources.
• Revoking compromised credentials or isolating affected devices.
• Keeping security logs to support investigation and response.
Professionals exploring the future of Zero Trust Architecture can consider the PG Certificate in Applied Generative Engineering & LLM Applications to build practical skills in generative AI and LLMs for developing intelligent, AI-powered applications.
What are the future trends in zero trust architecture in 2026?
In 2026, zero trust architecture is becoming more relevant as organizations manage cloud services, distributed workforces, automated workflows, and AI systems. Security teams are increasingly focusing on identity, real time risk signals, and automated responses rather than relying only on network level protection.
The following trends show how organizations can strengthen access control while keeping security practical for everyday operations.
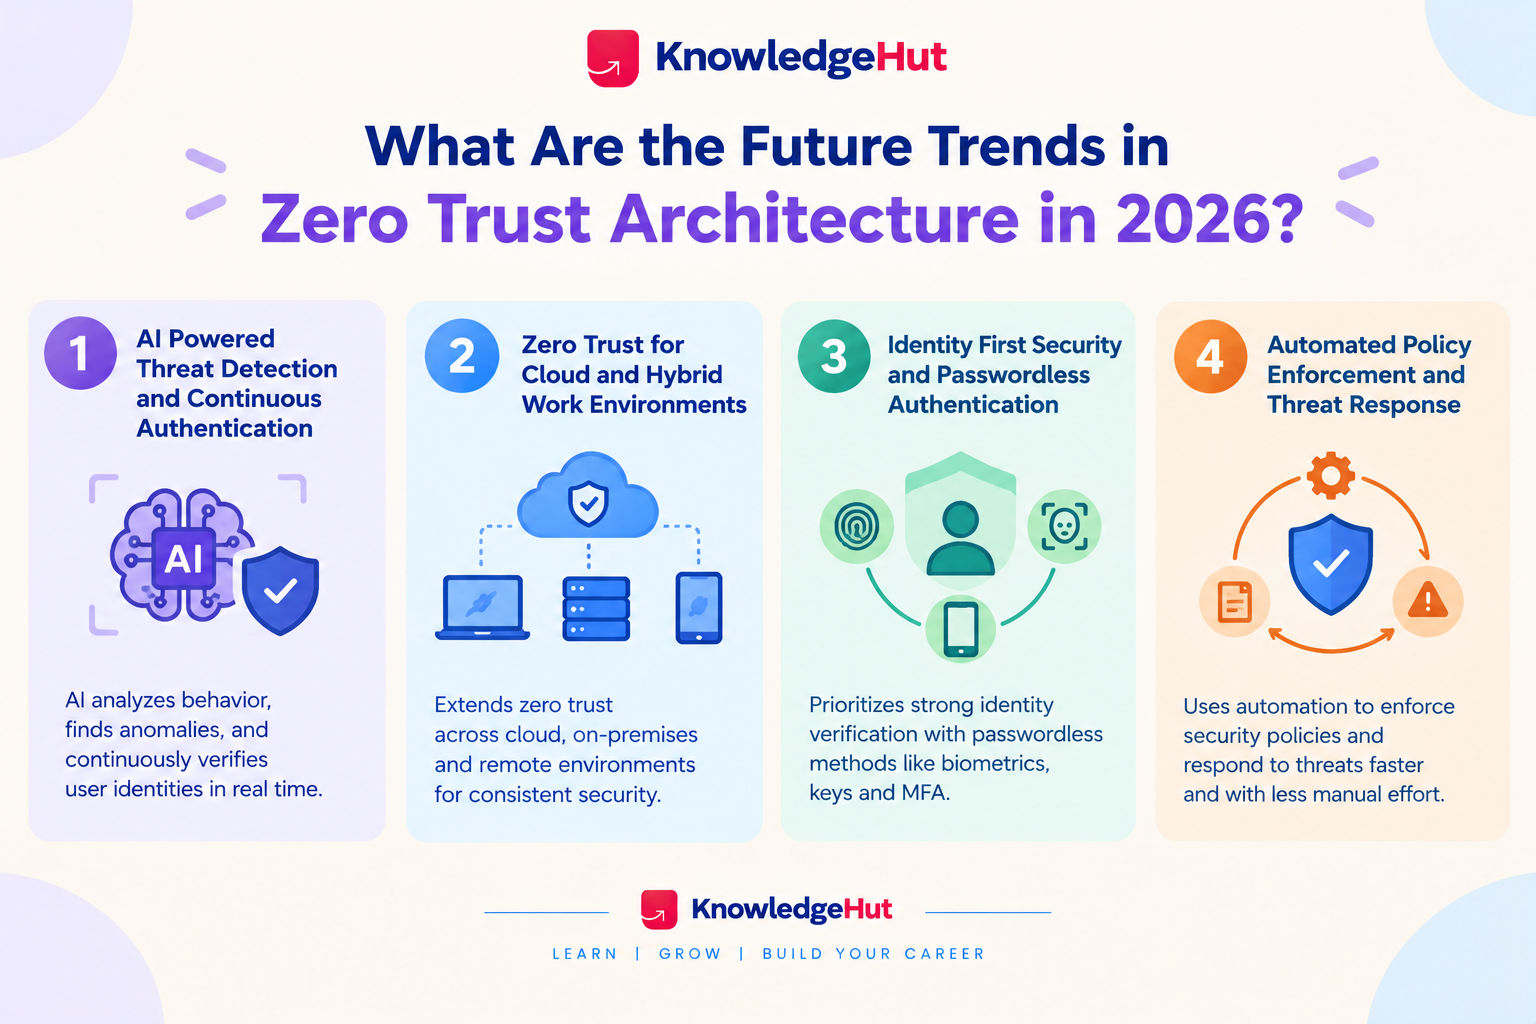
1. AI powered threat detection and continuous authentication
AI supported security tools can analyze large volumes of activity to identify patterns that may indicate compromised accounts, unusual access, or emerging threats. When combined with zero trust controls, these insights can help teams review access decisions and respond more quickly.
Possible applications include:
• Identifying unusual login patterns or access attempts.
• Flagging unexpected changes in user or application behavior.
• Supporting risk based authentication decisions.
• Helping analysts prioritize alerts that need investigation.
2. Zero trust for cloud and hybrid work environments
Cloud applications, remote devices, and on premises systems often operate across different environments. This creates challenges for organizations that rely on a single network boundary to control access.
Zero trust helps apply security policies consistently, regardless of where a user or resource is located.
Important areas of focus include:
• Verifying users and devices connecting from outside the office.
• Applying access controls to cloud applications and storage.
• Protecting connections between on premises infrastructure and cloud services.
• Monitoring access across multiple platforms through centralized security tools.
3. Identity first security and passwordless authentication
Identity is a central part of modern access control because attackers often target passwords, sessions, and user accounts. Organizations are therefore placing more emphasis on verifying identities and strengthening authentication methods.
Passwordless options, such as passkeys and security keys, can reduce dependence on traditional passwords when implemented with suitable safeguards.
Key developments include:
• Using phishing resistant authentication for sensitive accounts.
• Applying multifactor authentication based on risk and access requirements.
• Managing identities for employees, contractors, applications, and AI agents.
• Reviewing permissions when employees change roles or leave the organization.
4. Automated policy enforcement and threat response
As organizations manage more applications and devices, manually reviewing every access decision becomes difficult. Automated policy enforcement can help apply security rules consistently and respond when an access request or session becomes risky.
For example, a security platform may require additional authentication, restrict a session, or isolate a device when it detects a serious risk signal.
Common uses include:
• Applying access policies consistently across connected systems.
• Removing permissions that are no longer needed.
• Revoking sessions associated with suspected account compromise.
• Connecting identity, endpoint, and threat monitoring tools.
• Recording automated decisions for audit and investigation.
Also read: Zero Trust Security
What are the benefits of zero trust architecture?
Zero trust architecture helps organizations control access based on verified identity, permissions, and current risk. It does not eliminate every cyber threat, but it can reduce unnecessary access and help security teams detect or contain incidents more effectively.
Its main benefits include stronger access control, better visibility, and more consistent protection across modern IT environments.
1. Reduced risk of unauthorized access and data breaches
Strict access controls help prevent users or compromised accounts from reaching resources they do not need. This reduces the opportunities available to attackers who gain access through stolen credentials or other weaknesses.
Key benefits include:
• More controlled access: Users receive permissions based on their roles and requirements.
• Better visibility: Security teams can review access activity and identify suspicious requests.
• Reduced exposure: Sensitive data and applications can be protected with additional controls.
• Faster access changes: Permissions can be adjusted or revoked when circumstances change.
2. Improved protection against ransomware and insider threats
Ransomware and insider threats can cause significant damage when an attacker or unauthorized user gains broad access to systems. Limiting privileges and separating important resources can make it harder for threats to spread.
A well planned implementation can help organizations:
• Restrict access to critical systems and sensitive information.
• Detect unusual activity involving privileged accounts.
• Limit unnecessary connections between devices and applications.
• Revoke access when an account or device is suspected of being compromised.
3. Stronger security for remote work and BYOD
Remote employees and bring your own device (BYOD) policies can make traditional network based security difficult to maintain. Employees may access company resources from home, public networks, personal devices, or different locations throughout the day.
Zero trust architecture helps address these situations by evaluating each access request instead of assuming that a connection is safe.
Organizations can benefit from:
• Checking whether a device meets security requirements.
• Restricting access from devices that do not meet company policies.
• Giving employees access only to the applications they need.
• Applying consistent controls to office based and remote users.
As Zero Trust Architecture increasingly relies on data-driven threat detection and intelligent security analytics, the Executive Post Graduate Certificate in Data Science and Applied AI can help professionals build relevant skills in data science, machine learning, and applied AI.
What are the challenges of implementing zero trust architecture?
Adopting zero trust architecture involves more than installing a new security tool. Organizations need to understand their existing systems, improve identity management, define access policies, and coordinate controls across teams.
The challenges can be managed through phased implementation, clear ownership, and regular reviews rather than attempting to change every system at once.
1. Legacy system integration and infrastructure complexity
Older applications and infrastructure may not support modern authentication, detailed access policies, or continuous monitoring. Connecting them to newer security tools can require additional configuration or upgrades.
Common challenges include:
• Limited compatibility: Some legacy systems may not support modern identity protocols or multifactor authentication.
• Fragmented infrastructure: Different departments may use separate identity systems and security tools.
• Incomplete visibility: Organizations may not know every application, device, service account, or data repository that needs protection.
• Integration risks: Changes to access controls may affect existing applications or business workflows.
2. Implementation costs and operational overhead
Implementing zero trust can require investment in identity management, endpoint security, network controls, monitoring, staff training, and system integration. The amount of work depends on the organization's size, current infrastructure, and security requirements.
Costs may include:
• New or upgraded security tools.
• Time spent reviewing users, permissions, and applications.
• Integration and migration work.
• Staff training and policy maintenance.
• Ongoing monitoring and incident response.
3. User experience and access management challenges
Strict access policies may frustrate employees when legitimate requests are repeatedly blocked or authentication requirements are difficult to use. Poorly planned controls can also create extra work for IT teams and slow business processes.
To maintain a reasonable balance between security and usability, organizations should:
• Explain new authentication and access requirements clearly.
• Use role based access to avoid granting excessive permissions.
• Test policy changes with a small group before wider deployment.
• Provide a secure process for requesting additional access.
• Review repeated access failures and legitimate exceptions.
Also read: Zero Trust – Continuous Authentication in Cybersecurity
Conclusion
Zero trust architecture is ideal for organizations seeking stronger access control across cloud systems, remote work, and sensitive data. Organizations with legacy systems or limited resources should start with critical assets, strengthen authentication, and implement least privilege access gradually to improve security without disrupting daily operations.
Have A Query? Get in Touch With Our Customer Support | upGrad KnowledgeHut
Frequently Asked Questions (FAQs)
1. What is the difference between zero trust architecture and traditional network security?
Traditional network security often relies on a secure network perimeter to protect internal resources. Zero trust architecture verifies every access request based on identity, device status, permissions, and risk. This reduces the risk of unauthorized access, even when a user is already connected to the company network.
2. Does zero trust architecture replace a VPN or firewall?
No, zero trust architecture does not necessarily replace VPNs or firewalls. These technologies can still protect network connections and control traffic, while zero trust adds identity based verification and least privilege access. Organizations should choose controls based on their security requirements and existing infrastructure.
3. How can an organization measure the success of a zero trust implementation?
Organizations can measure progress by tracking unauthorized access attempts, access policy violations, incident response times, and the number of excessive permissions removed. They can also monitor multifactor authentication coverage and the percentage of critical assets protected. Regular reviews help determine whether zero trust architecture is reducing security risks.
4. What are the first steps to implementing zero trust architecture in an organization?
Start by identifying critical data, applications, devices, users, and existing security gaps. Strengthen identity verification, enable multifactor authentication, and apply least privilege access to sensitive resources. A phased rollout helps organizations test policies and expand zero trust architecture without changing every system at once.
5. Can small businesses implement zero trust architecture with a limited budget?
Yes, small businesses can adopt zero trust architecture gradually without investing in a large security platform immediately. They can begin with multifactor authentication, role based permissions, device updates, and regular access reviews. Using existing security features and prioritizing critical resources can help control costs.
6. What tools and technologies are needed to build a zero trust architecture?
Common technologies include identity and access management, multifactor authentication, endpoint protection, network segmentation, and security monitoring tools. Organizations may also use zero trust network access (ZTNA) and security information and event management (SIEM) solutions. The right combination depends on existing systems, business needs, and risk levels.
7. How does zero trust architecture support regulatory compliance and data privacy?
Zero trust architecture supports compliance by restricting access to sensitive information, enforcing permissions, and improving visibility into user activity. Access logs can also help organizations demonstrate how resources are protected during audits. However, zero trust alone does not guarantee compliance; organizations must still meet the specific requirements of applicable laws and standards.
8. Can zero trust architecture prevent all cyberattacks?
No, zero trust architecture cannot prevent every cyberattack. It helps reduce unauthorized access and limit the spread of threats through continuous verification, least privilege access, and monitoring. Organizations still need additional safeguards, including endpoint security, backups, employee awareness, and incident response planning.
9. How can organizations implement zero trust without disrupting existing business operations?
Organizations should begin with a limited pilot involving selected users, applications, or high risk resources. They can test access policies, identify compatibility issues, and gather user feedback before expanding the rollout. Gradual implementation, clear communication, and fallback procedures help minimize disruption.
10. What is the difference between zero trust architecture and zero trust network access (ZTNA)?
Zero trust architecture is the broader security model built around continuous verification, least privilege access, and the assumption of potential compromise. ZTNA is a technology approach that applies these principles to control access to specific applications and resources. In other words, ZTNA can be one component of a broader zero trust architecture.
1668 articles published
KnowledgeHut is an outcome-focused global ed-tech company. We help organizations and professionals unlock excellence through skills development. We offer training solutions under the people and proces...
Get Free Consultation
By submitting, I accept the T&C and
Privacy Policy